Security and UK GDPR
Drawn handles health data, so it's built to that standard. It runs in London, encrypts patient data, keeps each clinic's data apart, needs a one-time code for every staff sign-in, and records every access to a record. Your clinic stays in control of its patients' data.
- Hosted in London
- Data processing agreement
- No trackers
Where your data is
- London, UKDrawn's pages, server code and database
- Stockholm, SwedenLab report files, encrypted
- IrelandEmails: confirmations, reminders and sign-in codes
HTTPS everywhereEncrypted at restNo trackers
Responsibility
Who is responsible for patient data?
Your clinic is the controller of your patients' data, and Drawn is your processor. We handle it only on your instructions, under a data processing agreement you accept when you sign up. Drawn treats all booking data as health data, and protects it to that standard. Every company we use is listed on our sub-processors page.
Controller
Your clinic
Decides why patient data is collected, and how it's used.
Processor
Drawn
Handles it only on your instructions, and protects it as health data.
Protection
How patient data is protected
Encryption
HTTPS with HSTS for every connection, verified TLS to the database, and encryption at rest. Report files use keys in AWS Key Management Service.Who can see what
Each clinic's data is kept apart by row-level security. Staff see only what their role needs, and reports only clinicians and staff given access.Signing in
Staff passwords of at least 12 characters, plus a one-time code by email on every sign-in, and rate limits on repeated attempts.Collecting less
Date of birth only if your clinic switches it on, with a reason patients see. No analytics or advertising trackers.An audit log you can't edit
Views, downloads, exports, changes and deletions of records are logged, by ID only. Entries can't be altered.Deleted on time
Records are deleted automatically on the retention periods your clinic sets. There's no keep forever option.
In numbers
The details that keep records private
Report download links expire quickly, sessions end on their own, and the audit log records every view, download, export and change of a record.
- characters for every staff password
- 12+
- before a report link expires
- 60s
- staff and patient sessions
- 8h · 2h
- the audit log is kept
- 24 mo
Messages
No test names on lock screens
By default, texts, emails and links never name the tests a patient booked, because inboxes and phones are often shared or seen by others. Patients see what to expect when they open their booking, not on their lock screen.
08:02
Monday 2 November
Northvale Diagnosticsnow
Reminder: your appointment is tomorrow at 08:00. See how to prepare: your booking link.
Data requests
Patients' requests, handled in one place
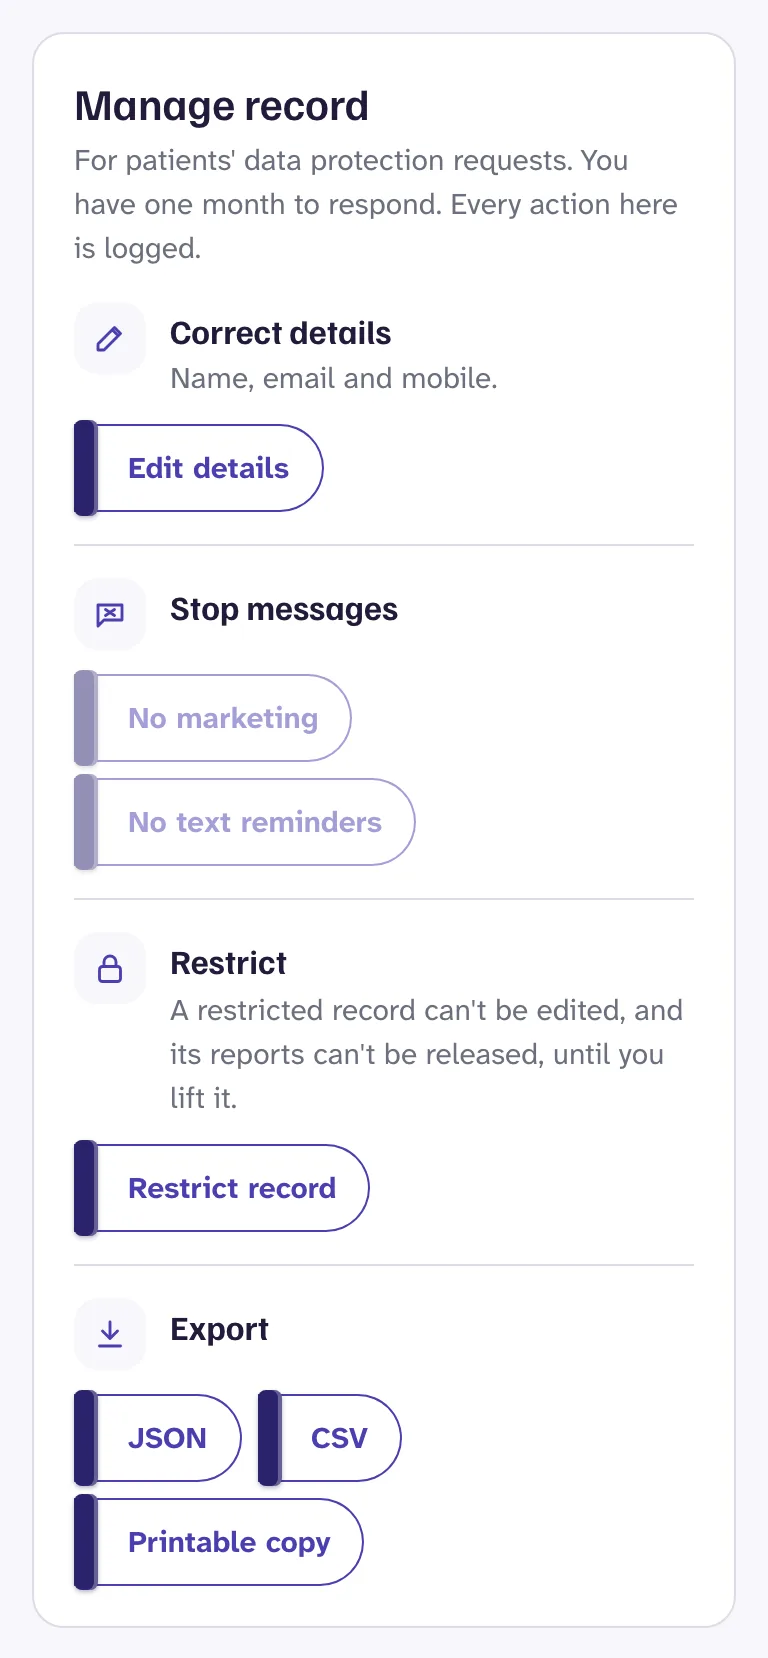
When a patient asks to see, correct, restrict or delete their data, your team handles it from their record: a printable copy, an export as JSON or CSV, corrections, a restriction, or deletion. Every action is logged. See Privacy and patient data.
Questions
Questions clinics ask
Something else? Email director@hizmedia.com and a real person will reply.
Is Drawn UK GDPR compliant?
Drawn is built for UK GDPR. It acts as your processor under a data processing agreement, keeps its database in London, treats booking data as health data, and gives your team tools for data protection requests.
Where is patient data stored?
The database is in London. Lab report files are stored in Stockholm, Sweden, and emails are sent from Ireland.
Do staff need two-factor sign-in?
Yes. Every staff sign-in needs a password of at least 12 characters and a one-time code sent by email.
Does Drawn use tracking cookies?
No. Drawn has no analytics or advertising trackers.
Take your first booking this afternoon
Sign up, add your tests and hours, and share your link. 14 days free, no card needed.